Prevent Patient Data Breaches: Why Healthcare Insider Threat Awareness Matters
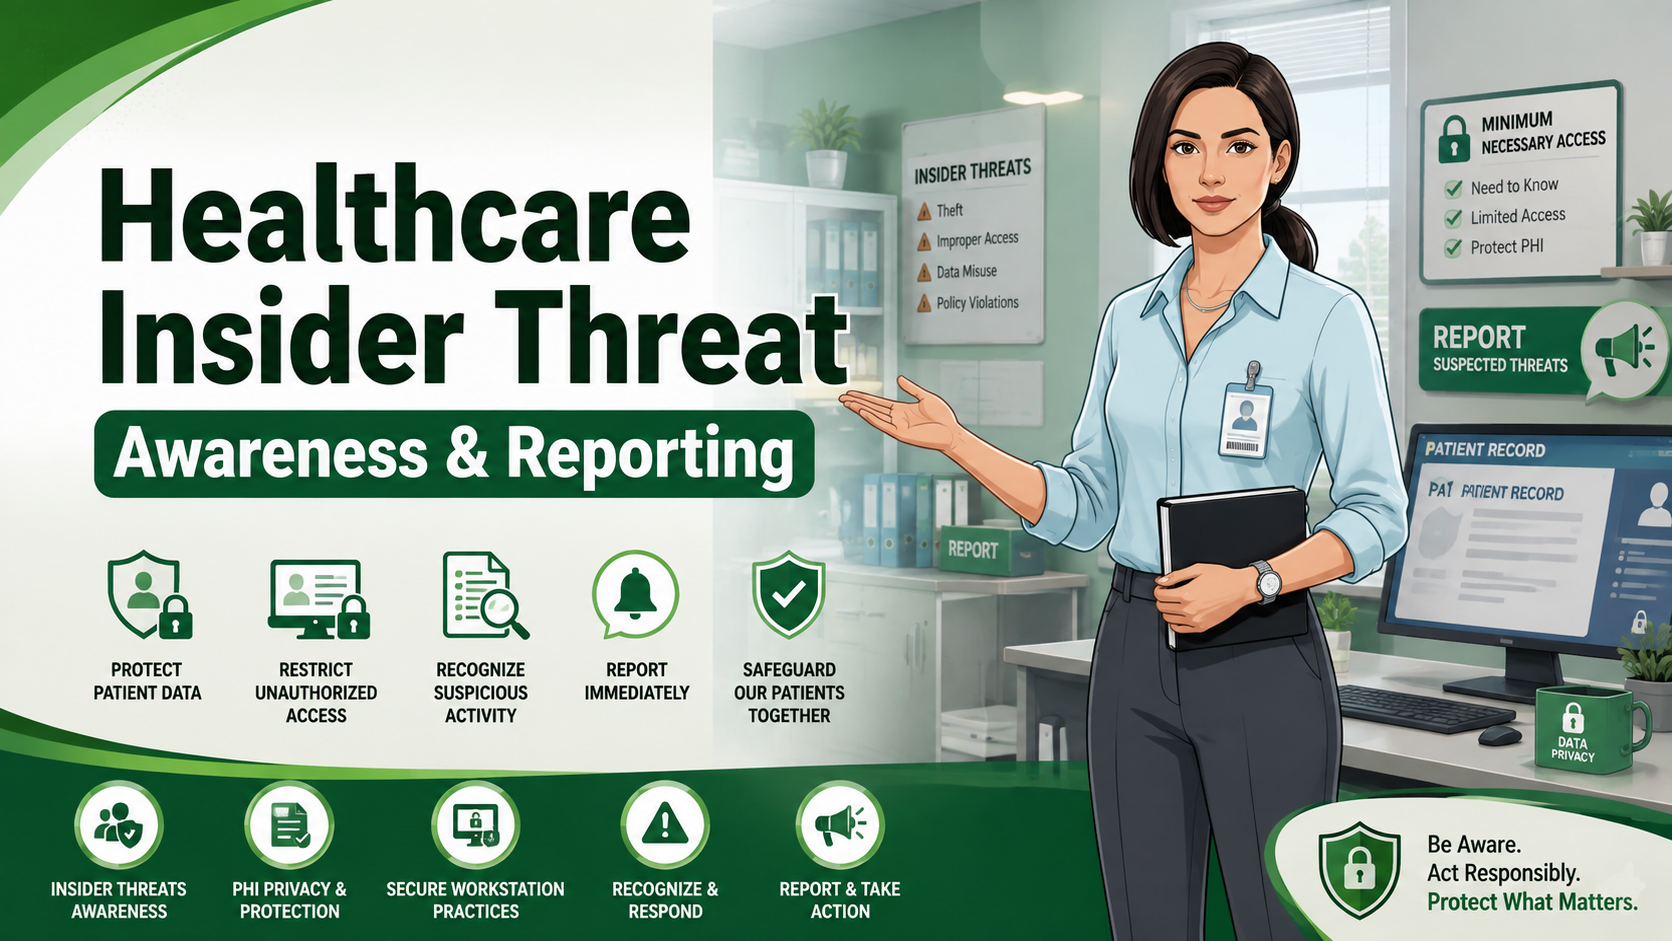
This Healthcare Insider Threat Awareness & Reporting course is a core part of any healthcare cybersecurity awareness program, empowering non-clinical healthcare professionals to spot threat indicators, safeguard PHI, and execute swift reporting protocols.
Delivered as a video-based, interactive SCORM course with narrated storytelling, game checkpoints, and quizzes, it builds a practical, workplace-ready foundation in insider threat types, HIPAA compliance, and escalation workflows, helping reduce data breaches, HIPAA non-compliance penalties, and legal liability
Who This Course Is For
Ideal for general employees, business users, team leaders, and department members who handle sensitive patient information, such as HR, billing, administration, and front-desk staff, but lack a technical cybersecurity background. Healthcare Insider Threat Awareness Training is becoming a standard part of workplace compliance and professional development, alongside information security and data privacy training.
What Learners Will Master
- Identify Insider Threat Types: Distinguish between malicious, negligent, and compromised insider threats using frameworks aligned with CISA Insider Threat Mitigation Guidance, understanding that unintentional mistakes can also cause security incidents.
- Recognize Red Flags: Spot indicators of potential threats, such as unusual access patterns, secretive conduct, or accessing information outside job scope.
- Apply HIPAA Standards: Understand the practical application of the HHS HIPAA Minimum Necessary Standard for accessing PHI, and why curiosity-driven access violates compliance.
- Understand Reporting Procedures: Master protocols for reporting suspicious activity and escalating concerns to management and security contacts with psychological safety.
- Case Study Analysis: Review realistic workplace scenarios and escalation patterns to reinforce threat mitigation best practices.
Engage Learners with Interactive Microlearning
Ditch static slide decks for dynamic storytelling. This 39-minute video-based, interactive SCORM course uses rich media to maximize retention:
- Narrated Video Scenarios: Real-world workplace examples breaking down threat identification, red flags, and escalation procedures.
- Gamified Insider Threat Training: Fact/Fiction card games, drag-and-drop activities, and reflex games testing risk recognition and behavioral hazards.
- Knowledge Check & Certification: End-of-course quiz requiring an 80% passing score before completion tracking in your LMS.
LMS Compatibility & Technical Specifications
Works out of the box with any major LMS (Cornerstone, Docebo, Moodle, Canvas, SuccessFactors, and more).
- Format: Video-based, interactive SCORM course
- Standards Supported: SCORM 1.2 & SCORM 2004 (full ZIP package included)
- Duration: 39-minute microlearning
- Accessibility: WCAG 2.1 AA compliant
- Instant Access: Download immediately after purchase, or request an enterprise preview file